
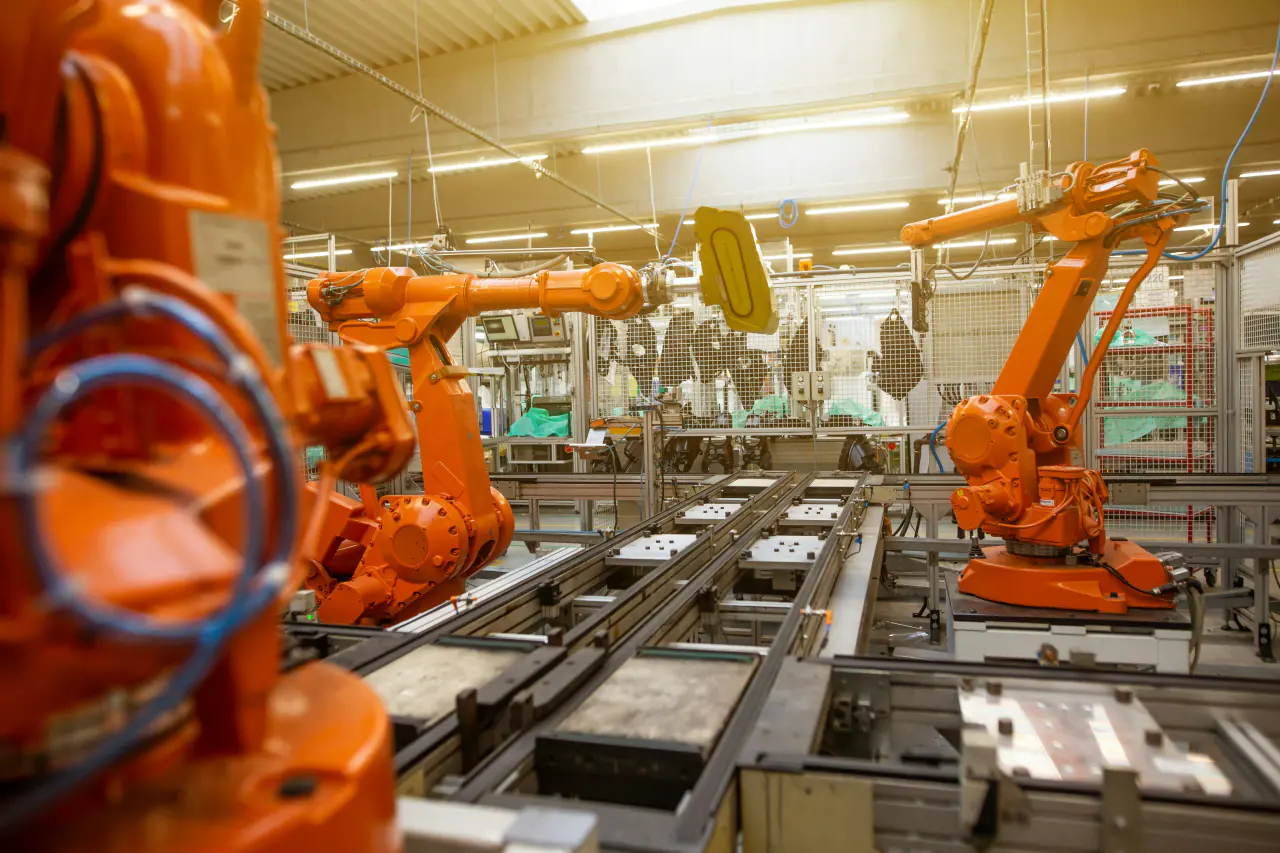
Industrial cybersecurity decisions have to account for production consequence, maintenance windows, supplier dependency and equipment that cannot be patched or restarted on demand.
The underlying assessment records the installed architecture and operating evidence before recommending changes. Actions that need design, outage or supplier approval are separated from immediate corrections.